All Software
10 results
Pointer Lab
Memory scanner & debugger for Windows
An open-source alternative to Cheat Engine, written from scratch. Scan a running
game’s memory, find what writes to a value, walk the pointer chain, and patch the
instruction responsible. It ships with an auto-assembler, a structure dissector, a
speed hack, trainer export, an embedded Lua console, and a built-in tutorial to
learn on. Since 3.1.0 it also speaks MCP, so an AI agent can drive the same live
session you are looking at.
Memory Scanner
Debugger
C++20
Windows
View Details →
Signature Lab
Signature maker plugin for x64dbg
Select an instruction in x64dbg, press Alt+Shift+S, and get a byte signature that
finds the same code after the next update. It decodes every instruction to wildcard
the addresses that move and keep the code that does not, checks the result against
the whole module, and says why each byte was masked. When the code is not unique, it
signs the code that refers to it instead. Output in x64dbg, IDA, code+mask, C++ and
Pointer Lab forms.
x64dbg Plugin
Signature Scanning
C++20
32 & 64-bit
View Details →
sigscan
Byte-signature scanner library and CLI
Give sigscan a byte signature in x64dbg, IDA, code+mask, C++ array or
aobscanmodule form, and it finds it. It searches a byte buffer, a PE file on
disk, or a module in a running process. A pattern it cannot read is refused with a
reason, not reported as “not found”. The library is one C++20 header with no
dependencies, and sigscan.exe puts it on the command line. It reads every
form Signature Lab writes.
Signature Scanning
Header-Only Library
C++20
32 & 64-bit
View Details →
iretable-tools
Command-line toolkit for Pointer Lab project files
A command-line toolkit for the
.iretable project files Pointer Lab saves.
Convert a Cheat Engine .CT table into one, and export back where the fields
map. Every field that does not carry across is listed. Diff two tables, shift fixed
addresses after the main module moves, and lint a file before you open it. It works on
files only and never opens a process.
Pointer Lab
Cheat Engine Import
Command Line
C++20
View Details →
hookscan
Read-only hook scanner for Windows processes
Point it at a running process and it lists the code, import and export entries that no
longer match the files on disk. It applies each module’s relocations before it
compares, so a moved pointer is not a patch. Each patch is decoded, and its jump is
followed to the module it lands in. It opens the target read-only and never writes to
it. Output is a text report or JSON.
Hook Detection
Command Line
C++20
32 & 64-bit
View Details →
debug-bench
Anti-debug self-test target for Windows
Run it and it tries thirty well-known anti-debug checks on its own process. It prints
which ones fired and the raw value each one read. Attach a debugger and watch checks
start to fire. Turn on a debugger-hiding plugin and watch which ones go quiet. Each
check explains what it detects and when it gives a false positive. It is a self-test,
not a bypass, and it touches no other process.
Anti-Debug Checks
Test Target
C++20
32 & 64-bit
View Details →
pe-mcp
MCP server for static analysis of PE files
Register it with one command, and an AI agent can read an
.exe,
.dll or .sys file before the program runs. It lists headers,
sections, imports, exports, strings and resources. It disassembles x86 and x64 code and
finds every instruction that refers to an address. Its find_pattern tool
checks a signature against the file. Every answer is compact, paged JSON of 24 KB or
less, and it never opens a process or writes a byte.
MCP Server
Static Analysis
PE Files
C++20
View Details →
claude-game-re-plugin
Game reversing plugin for Claude Code
Install it, attach Pointer Lab to a program you own, and ask Claude to find a value,
find what writes it, walk its pointer chain or sign the instruction. Eight skills give
Claude the procedure for each job, taken from the Handbook’s chapters. Reads and
scans run freely. A hook blocks every tool that would change the target’s memory
or code until you opt in. The plugin also starts pe-mcp, so Claude can read the file on
disk.
Claude Code Plugin
Skills & Commands
Write Guard
Windows
View Details →
procpcap
Per-process packet capture for Windows
Capture one Windows program’s network traffic and open it in Wireshark. procpcap
watches the WinDivert FLOW layer to learn which process owns each connection, and
keeps only that process’s packets. Connections that were open before the capture
started are seeded from the Windows TCP and UDP tables. Every packet in the pcapng
carries the owning process ID and name. A live stats line shows payload entropy, so
you can tell encrypted traffic from something you can read.
Packet Capture
Wireshark
WinDivert
C++20
View Details →
openxr-pose-layer
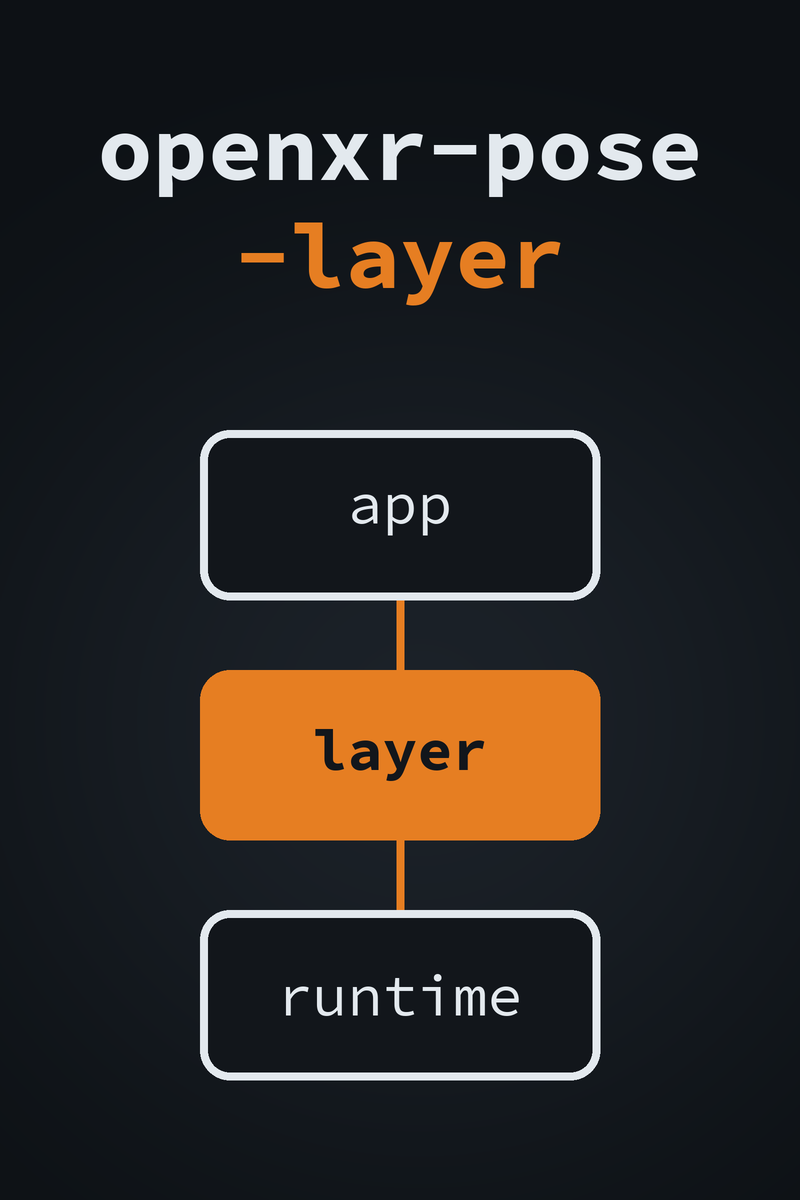
Record and replay OpenXR tracking
An OpenXR API layer that sits between a VR app and the runtime. In log mode it prints
the tracking and input calls the app makes, with timings. In record mode it saves every
frame’s head pose, eye views, controller poses and action states. In replay mode it
feeds them back, so the same motion runs again with no headset moving.
poseplay summarizes, dumps and trims the recordings.
OpenXR API Layer
VR
Record & Replay
C++20
View Details →